Executive Summary
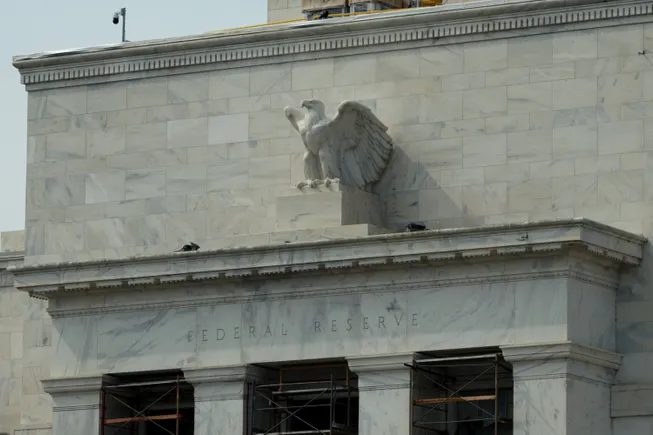
A scathing report from the Federal Reserve Board’s Office of Inspector General (OIG) has unveiled significant systemic vulnerabilities within the central bank’s information security infrastructure. The report, which details the mishandling of highly sensitive Federal Open Market Committee (FOMC) data, highlights a pattern of recurring security violations by a single employee that went unaddressed for years. The findings reveal a disturbing culture of administrative inertia, unclear reporting lines, and a failure to enforce established data protection protocols during the critical offboarding process.
The incident centers on a departing employee within the Division of International Finance who, throughout their final years of tenure, repeatedly bypassed security controls to move classified material. While the OIG stopped short of initiating a formal misconduct investigation into the final 2024 departure incident—citing the prevalence of "false positive" alerts that muddied the waters—the watchdog emphasized that the case serves as a diagnostic tool for much deeper, systemic rot within the Board’s oversight mechanisms.
Chronology of a Security Breach
The timeline of the employee’s actions paints a picture of a persistent disregard for information security protocols, compounded by the Federal Reserve’s failure to implement corrective measures.
2021: The Unencrypted USB Incident
The first major red flag emerged in 2021, when the Board’s information security operations team flagged that the employee had copied sensitive FOMC classified files onto an unencrypted USB drive. When confronted, the employee claimed the action was a mistake, asserting they had intended to use an encrypted device for file backups. Despite the sensitivity of the data, the incident appears to have been treated as an isolated lapse rather than a precursor to a behavioral pattern.
2023: The Email Exfiltration Attempt
Two years later, the same employee attempted to transmit classified FOMC information to a personal email account. Once again, the employee claimed the action was "inadvertent." By this stage, the employee had been previously counseled on the mandatory use of secure, encrypted storage for sensitive data. Despite these warnings, the employee continued to handle classified material in a manner that directly violated the Board’s established data loss prevention (DLP) policies.
2024: The Retirement and Restricted Travel
In February 2024, the employee announced their upcoming retirement. Alarmingly, they simultaneously expressed a desire to remove files from the system before their departure—a request that should have triggered immediate scrutiny given their history.
The situation escalated in June 2024, when the employee traveled to a country explicitly designated by the Federal Reserve Board as "restricted." The Division of International Finance was reportedly entirely unaware of this travel. During this window, the employee continued to engage in the unauthorized removal of information, a process that persisted into their official retirement in July 2024. The OIG did not become fully aware of the extent of this breach until July 2025, a full year after the employee had exited the institution.
Supporting Data and Institutional Deficiencies
The OIG’s report is not merely a critique of a single individual’s actions; it is a clinical dissection of how a large, complex organization like the Federal Reserve failed to communicate internally.
The Myth of "False Positives"
A significant factor in the delayed response was the reliance on automated alerting systems. The Board’s security teams often struggle with a high volume of "false positive" alerts, which monitor potential data exfiltration. The OIG found that these alerts have become so commonplace that they are often dismissed as routine noise rather than potential threats. In this instance, the lack of human intelligence and contextual analysis—specifically, the lack of awareness regarding the employee’s high-risk profile—allowed the actual breach to hide in plain sight among thousands of benign events.
Governance and Accountability Gaps
The OIG identified a total lack of clarity regarding which division was responsible for what. The report notes that there is no consensus among various groups at the Fed regarding "escalation and resolution responsibilities." This ambiguity meant that when an alert was triggered, it was shuffled between departments, with each assuming the other had handled the oversight. This "collective lack of action" led to a situation where the risks were allowed to accumulate, unchecked, for over 12 months.
Implications for Federal Information Security
The implications of these findings extend far beyond the Division of International Finance. The Federal Reserve holds some of the most sensitive economic and market-moving information in the world. The ability of a single employee to repeatedly circumvent security controls suggests that the current "defensive posture" of the central bank is brittle.
The Risk of Future Breaches
The OIG warned that unless the Board moves away from its current siloed approach, the risk of a "major information security breach" remains high. The report stresses that the lack of a "sense of shared responsibility" creates blind spots that sophisticated actors—or even disgruntled insiders—can easily exploit. If the Board cannot manage the offboarding of an employee with a known history of security infractions, it raises questions about its capacity to detect more complex, external cyber-espionage efforts.
Legal and Policy Hurdles
The OIG’s inability to pursue a formal misconduct investigation highlights a weakness in the Fed’s internal policy framework. When policies are not clearly linked to disciplinary consequences, and when documentation of past infractions (like the 2021 and 2023 incidents) does not effectively inform future risk assessment, the entire governance structure becomes toothless.
Official Responses and Remediation Plans
In response to the OIG’s findings, the Federal Reserve Board has concurred with all recommendations provided by the auditors. Recognizing the severity of the institutional failure, the central bank has committed to a multi-year overhaul of its security protocols.
The Roadmap to 2027
The Board’s remediation strategy is aggressive, focusing on both human-centric processes and technical infrastructure:
- Defining Roles and Responsibilities: By the first quarter of 2027, the Fed plans to implement comprehensive protocols that define exactly which teams are responsible for monitoring, escalating, and resolving potential security incidents. This is designed to eliminate the "conflicting understanding" of duties that allowed the 2024 incident to remain unresolved for so long.
- Next-Generation Data Loss Prevention (DLP): By the third quarter of 2027, the Board intends to roll out an enhanced monitoring capability as part of a new data loss prevention solution. This system is expected to provide better context to security alerts, reducing the "false positive" rate and allowing for more targeted, human-led investigations.
- Cultural and Procedural Alignment: Beyond technology, the Board has signaled an intent to foster a "shared responsibility" model. This includes training programs designed to ensure that management, human resources, and IT security act in concert when dealing with high-risk departures.
Conclusion: A Call for Cultural Change
The OIG’s report on the Federal Reserve’s offboarding failures is a sobering reminder that even the most robust technical security systems can be rendered ineffective by organizational dysfunction. The Fed’s reliance on automated tools without corresponding management accountability created a vacuum where sensitive FOMC information was left vulnerable.
As the central bank prepares to implement its 2027 security roadmap, the challenge will be to ensure that these changes are not merely administrative window dressing. True security at an institution of the Federal Reserve’s importance requires a vigilant, integrated, and proactive culture—one where security alerts are treated with the gravity they deserve, and where history is not allowed to repeat itself simply because of a lack of inter-departmental communication. For the Federal Reserve, the time for "counseling" and "inadvertent" excuses has passed; the era of strict accountability must now begin.