The AI Security Paradox: How Anthropic’s "Project Glasswing" is Rewriting the Patching Playbook

The landscape of cybersecurity is undergoing a seismic shift, driven by a paradoxical reality: while artificial intelligence platforms are increasingly being targeted by sophisticated social engineering, they have simultaneously become the most potent tools in the defender’s arsenal. This month, the global tech industry is witnessing the tangible consequences of this shift as software titans—including…
Read Full News

Digital Proxies of War: The Dutch Crackdown on Infrastructure Powering Russian Cyber-Operations

In a significant blow to the clandestine digital infrastructure supporting the Kremlin’s hybrid warfare, Dutch financial crime investigators have executed a high-profile raid, dismantling a network accused of facilitating Russian cyberattacks and disinformation campaigns across the European Union. On May 18, the Fiscal Intelligence and Investigation Service (FIOD) arrested two primary figures linked to the…

Read Full News

The Downfall of Scattered Spider: Two British Hackers Plead Guilty to Global Cyber-Terrorism

In a landmark development for international cybercrime enforcement, two key members of the notorious hacking collective "Scattered Spider" have pleaded guilty in a United Kingdom court. The pair, Thalha Jubair, 20, and Owen Flowers, 18, admitted to a string of devastating cyberattacks that crippled critical infrastructure, including London’s public transport network, and compromised major healthcare…

Read Full News

Critical Security Breach: CISA Contractor Exposes Sensitive Infrastructure via Public GitHub Repository

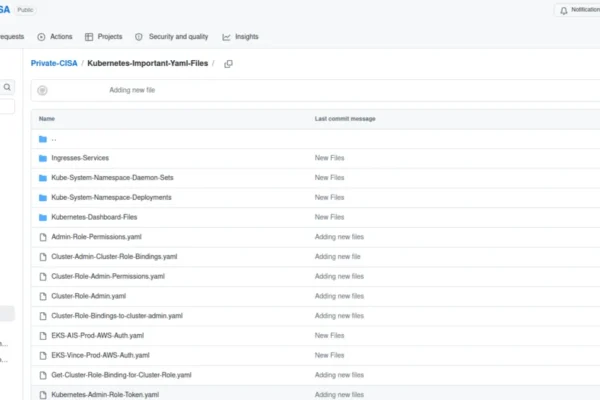
In a staggering lapse of operational security, a government contractor for the Cybersecurity and Infrastructure Security Agency (CISA) inadvertently exposed a treasure trove of highly sensitive credentials and internal deployment configurations to the public internet. The data, hosted in a public GitHub repository aptly named “Private-CISA,” included administrative access keys to critical AWS GovCloud accounts,…

Read Full News

The Fall of ‘Dort’: Inside the Collapse of the Kimwolf Botnet and the Arrest of its Mastermind

In a significant victory for international cybersecurity, Canadian authorities have apprehended a 23-year-old Ottawa resident accused of orchestrating "Kimwolf," a massive Internet-of-Things (IoT) botnet responsible for record-breaking distributed denial-of-service (DDoS) attacks. The arrest marks the culmination of a high-stakes, months-long investigation involving the Ontario Provincial Police (OPP), the U.S. Department of Justice (DOJ), and the…

Read Full News

Security Crisis at CISA: Congressional Leaders Demand Answers After Contractor Exposes Sensitive Agency Credentials

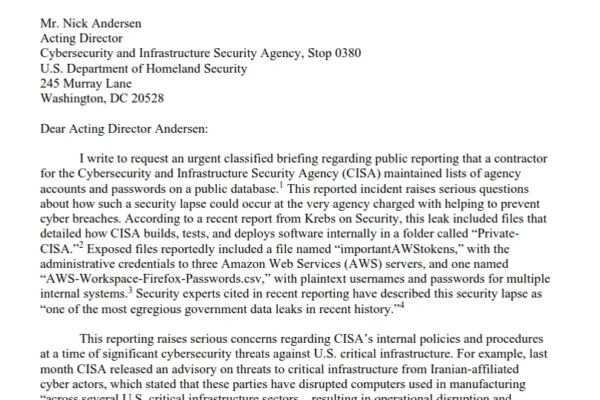
In a stunning security failure that has sent shockwaves through the federal government, the U.S. Cybersecurity & Infrastructure Security Agency (CISA)—the very entity tasked with safeguarding the nation’s digital defenses—has found itself at the center of a major data breach. Revelations emerged this week that a contractor for the agency inadvertently, yet flagrantly, exposed a…

Read Full News

The Age of AI-Driven Vulnerabilities: Microsoft’s Record-Breaking June Patch Tuesday

In a watershed moment for cybersecurity, Microsoft has released a monumental set of software updates, addressing nearly 200 security vulnerabilities across its Windows operating systems and associated software ecosystem. This June “Patch Tuesday” marks a record-breaking volume of fixes for the software giant, signaling a new, volatile era in threat management where the velocity of…

Read Full News

The Unmasking of ‘The Gentlemen’: How a Marketing Executive Became a Ransomware Kingpin

In the shadow-filled landscape of the dark web, few entities have risen with the meteoric speed and predatory efficiency of "The Gentlemen." Emerging as a formidable Ransomware-as-a-Service (RaaS) operation in mid-2025, the group has quickly cemented itself as the second most active ransomware syndicate globally. By rewriting the traditional rules of affiliate economics and leveraging…

Read Full News

The Silent Hijack: How Millions of Streaming Devices Became the Engine of a Global Proxy Botnet

For the past four years, a sprawling, shadow-like infrastructure known as Popa has operated beneath the radar of mainstream cybersecurity, turning millions of consumer Android TV boxes into involuntary relay stations for malicious internet traffic. While the name may not carry the notoriety of high-profile ransomware gangs, its reach is vast. Security researchers have now…

Read Full News