In an era defined by rapid technological evolution and complex digital ecosystems, the success of any information technology initiative hinges on one critical discipline: IT Project Risk Management. As businesses increasingly rely on software deployments, cloud migration, and intricate digital infrastructures, the margin for error has narrowed dramatically.
Effective risk management is no longer a passive administrative checkbox; it is a dynamic, proactive methodology designed to safeguard budgets, protect timelines, and turn potential vulnerabilities into strategic advantages. By systematically identifying threats—such as cybersecurity breaches, scope creep, and schedule delays—organizations can shield themselves from catastrophic financial losses and operational downtime.
The Anatomy of IT Project Risk: Main Facts
At its core, project risk management is the systematic process of identifying, analyzing, prioritizing, and mitigating uncertainties that could derail a project’s objectives. In the realm of IT, these uncertainties take many forms, ranging from internal technical hurdles to external regulatory shifts.

Defining the Landscape
When managing IT projects, leaders must recognize that risks are not merely negative events to be avoided; they can also represent hidden opportunities. The standard project risk management lifecycle encompasses several foundational pillars:
- Identification: Pinpointing potential vulnerabilities, including software bugs, infrastructure limitations, and human error.
- Assessment: Evaluating the likelihood of occurrence and the potential severity of impact.
- Response Planning: Developing targeted strategies to avoid, transfer, mitigate, or accept risks.
- Implementation and Monitoring: Actively tracking issues using centralized tools and continuously adjusting strategies as the project evolves.
According to industry metrics, proactive risk identification early in a project lifecycle can reduce the likelihood of costly delays and budget overruns by up to 20%. Furthermore, engaging diverse stakeholders during the risk assessment phase can expand problem-solving perspectives, increasing overall project opportunities and efficiency gains by roughly 30%.
The Chronology of the IT Risk Management Life Cycle
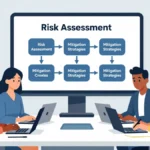
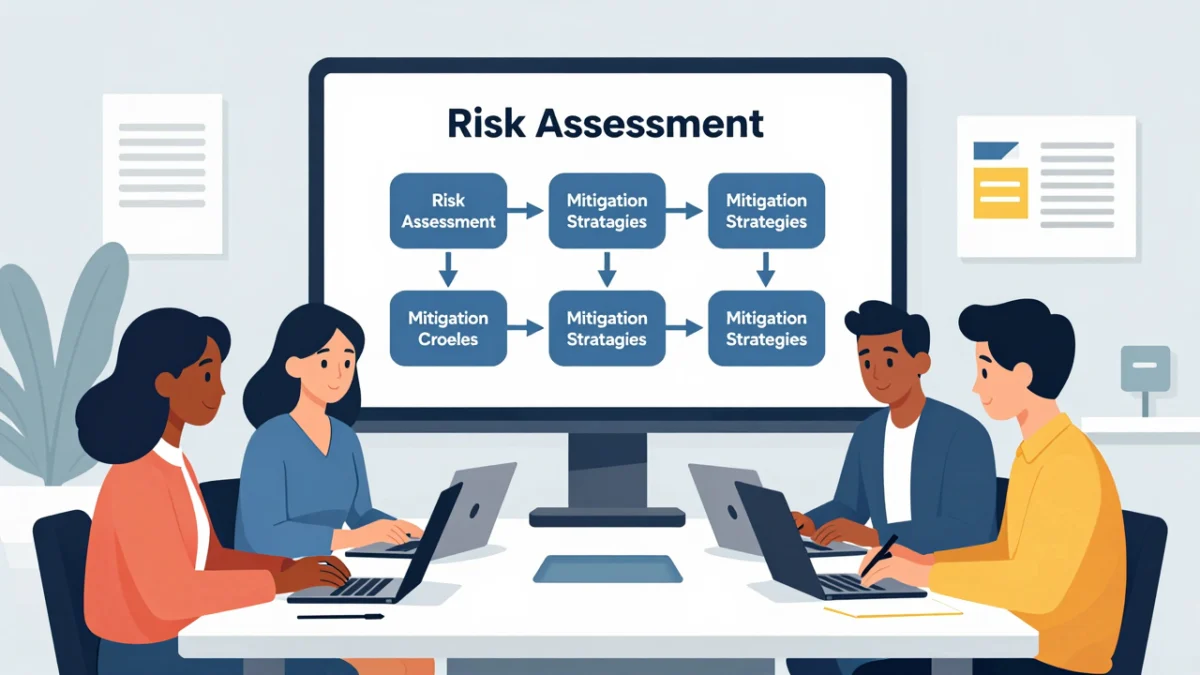
Integrating risk management into an IT project is not a one-time event; it is a continuous, five-stage evolutionary process that runs parallel to the project lifecycle.

[1. Identification] ➔ [2. Assessment] ➔ [3. Response Planning] ➔ [4. Implementation] ➔ [5. Monitoring]Stage 1: Identification
The journey begins at project inception. Project managers, team members, and stakeholders collaborate in brainstorming sessions and historical data reviews to map out potential obstacles. Common early-stage discoveries include resource shortages, regulatory compliance bottlenecks (particularly in sensitive sectors like healthcare and finance), and aggressive scheduling demands.
Stage 2: Assessment
Once threats are cataloged, they undergo qualitative and quantitative analysis. Techniques such as probability-impact risk matrices and Monte Carlo simulations help teams visualize which risks pose the greatest danger. This step ensures that limited resources are directed toward high-priority vulnerabilities rather than minor inconveniences.
Stage 3: Response Planning
Armed with analytical insights, project leaders craft concrete action plans. This phase involves deciding whether to mitigate a threat (e.g., implementing rigorous cybersecurity audits), transfer it (e.g., purchasing cyber insurance or outsourcing a volatile module), avoid it (e.g., changing project scope), or accept it (allocating contingency funds).

Stage 4: Implementation
Plans are put into motion. Risk owners are assigned to specific items documented in a centralized risk register. Tools such as Jira, Microsoft Project, and AI-driven platforms like IBM Watson are deployed to automate tracking, streamline team communication, and enforce accountability.
Stage 5: Continuous Monitoring and Control
As the project progresses through development, testing, and deployment, the risk landscape shifts. Regular risk audits and status reviews ensure that new vulnerabilities—such as sudden software incompatibilities or emerging regulatory mandates—are captured immediately, keeping the project aligned with its core goals.
Supporting Data and Mitigation Frameworks
To contextualize the financial and operational impact of structured risk management, organizations rely on empirical data and standardized mitigation matrices. Below is an overview of common IT project risks, their recommended countermeasures, and expected outcomes:

| Risk Type | Root Cause / Description | Recommended Mitigation Strategy | Expected Outcome |
|---|---|---|---|
| Cybersecurity | Vulnerable code, unauthorized access, malware | Conduct regular security audits and penetration testing | Reduce security incidents by up to 50% |
| Schedule Delays | Unrealistic timelines, scope expansion, bottlenecks | Set realistic milestones and modular delivery schedules | Minimize cascading project delays |
| Financial Overruns | Unforeseen costs, poor initial estimation | Create detailed, flexible budgets with contingency reserves | Limit unplanned expenses and margin erosion |
| Technology Adoption | Steep learning curves, incompatible legacy systems | Explore emerging tech pilots and comprehensive team training | Boost team productivity by 20% to 30% |
| Stakeholder Misalignment | Poor communication, shifting expectations | Establish regular feedback channels and clear governance | Enhance overall project support and buy-in |
The Power of Advanced Analytics
Modern IT risk management heavily integrates emerging technologies. Artificial intelligence and machine learning algorithms are increasingly embedded within project management tools to run predictive analytics. By analyzing historical project data, these systems can forecast where a project is likely to fail weeks before an issue manifests, allowing managers to intervene proactively.
Official Perspectives and Industry Standards
Global governance and quality control bodies consistently emphasize the integration of structured risk methodologies. Regulatory organizations, such as the Financial Industry Regulatory Authority (FINRA) and international health standards bodies, mandate stringent compliance protocols for technology integrations in regulated industries. Failing to account for regulatory compliance risks during the early stages of an IT project can result in severe legal penalties, halted deployments, and irrecoverable reputational damage.
Furthermore, professional organizations advocate for continuous professional development. Certifications in frameworks such as Agile, Six Sigma, and Project Management Institute (PMI) standards equip IT leaders with the sophisticated toolsets required to navigate modern software project complexities. Industry experts stress that communication remains the golden thread uniting these standards; transparent dialogues between developers, executives, and end-users ensure that risk perception remains universally understood across all tiers of an organization.

Operational Implications: Threats vs. Opportunities
While the primary objective of risk management is defense, a mature IT risk strategy also acts as an engine for innovation.
Mitigating Severe Threats
Left unchecked, technical risks like scope creep—where project requirements expand uncontrollably without adjustments to time, budget, or resources—can bankrupt an initiative. Similarly, unaddressed software bugs and hardware incompatibilities lead to cascading failures upon deployment. By enforcing rigorous testing, validation phases, and strict scope change request procedures, organizations protect their baseline investments.
Unlocking Strategic Opportunities
Conversely, confronting risk head-on often uncovers powerful opportunities. For instance, addressing a severe cybersecurity threat may require an organization to overhaul its legacy infrastructure, leading to the adoption of advanced cloud-native architectures. This modernization not only neutralizes the security threat but can dramatically enhance operational efficiency, resulting in productivity increases of up to 40% and revenue growth potential of nearly 30%.

External risks, such as sudden changes in market regulations or competitor moves, can similarly force an agile development team to pivot rapidly, granting the enterprise a decisive competitive edge.
Conclusion
IT Project Risk Management is the bedrock upon which successful digital initiatives are built. By transitioning from a reactive firefighting mindset to a proactive, structured framework of identification, assessment, response, and continuous monitoring, organizations can drastically curtail the financial and operational fallout of unexpected disruptions.
Leveraging essential tools—such as comprehensive risk registers, probability-impact matrices, and AI-driven analytics—empowers teams to maintain visibility and control throughout the project lifecycle. Moreover, fostering an organizational culture of open communication and stakeholder engagement ensures that every team member remains aligned against shared threats and primed to capture hidden opportunities.

Investing time, resources, and training into robust IT risk management strategies today guarantees resilient, cost-effective, and successful technological outcomes tomorrow.