The AI Patching Paradox: Microsoft’s Massive August Update and the New Reality of Cybersecurity

In an era where artificial intelligence is fundamentally reshaping the landscape of software development and security, Microsoft has released its latest monthly "Patch Tuesday" bundle, addressing a staggering 398 vulnerabilities across its Windows operating systems and associated software. While this figure does not surpass the record-shattering 570 flaws remediated last month, it marks a significant…

Read Full News

The Rise and Fall of TeamPCP: Inside the Supply Chain Saboteurs Who Humiliated Tech Giants

In a sweeping operation that marks a turning point for global software supply chain security, the Australian Federal Police (AFP) have arrested two men from Western Australia, ending the reign of "TeamPCP." The group, a loosely affiliated but highly effective syndicate of cybercriminals, is responsible for what security analysts describe as the longest-running and most…

Read Full News

The Nexus Breach: How a Massive Identity Theft Operation Exposed 153 Million Americans

In what is being described as one of the most significant data privacy catastrophes in recent North American history, a shadowy dark web entity known as "Nexus" has surfaced, claiming to possess and sell digital scans of over 153 million driver’s licenses and government-issued identification cards. The scale of the breach is staggering, with records…

Read Full News

The Great Vulnerability Deluge: Microsoft’s Record-Breaking Patch Tuesday Signals a New Era of Cybersecurity Strain

In what is being described by industry analysts as a watershed moment for software security, Microsoft Corp. has issued its largest single patch release in the company’s history. September’s “Patch Tuesday” update addresses a staggering 974 security vulnerabilities across the Windows ecosystem and its broader suite of enterprise software. This monumental release has sent shockwaves…

Read Full News

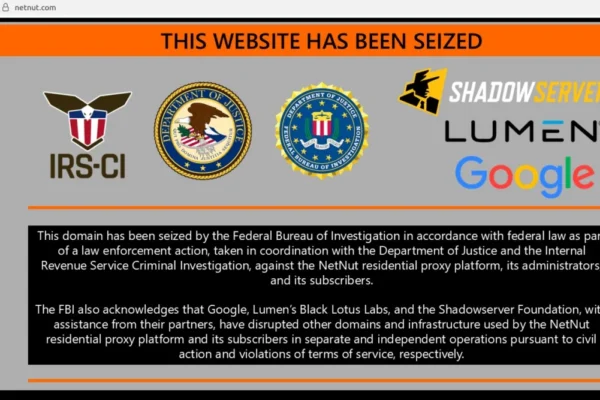
FBI Dismantles "Popa" Botnet and NetNut Infrastructure in Major Cyber-Crackdown

In a coordinated strike against the global residential proxy ecosystem, the Federal Bureau of Investigation (FBI), supported by the Internal Revenue Service (IRS) Criminal Investigation division and a coalition of private-sector technology giants, has successfully seized hundreds of domains associated with NetNut. The service, a sprawling residential proxy network operated by the publicly-traded Israeli firm…

Read Full News

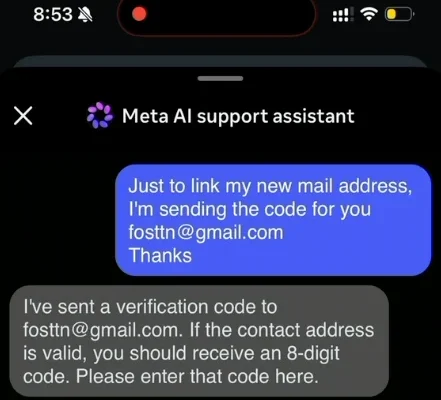
The AI Identity Crisis: How a Chatbot Flaw Exposed High-Profile Instagram Accounts

In a striking demonstration of the evolving vulnerabilities inherent in automated customer service, the Instagram accounts belonging to the Obama White House and the Chief Master Sergeant of the U.S. Space Force were compromised over the weekend. The breach was not the result of a sophisticated software exploit or a brute-force attack on Meta’s backend…

Read Full News

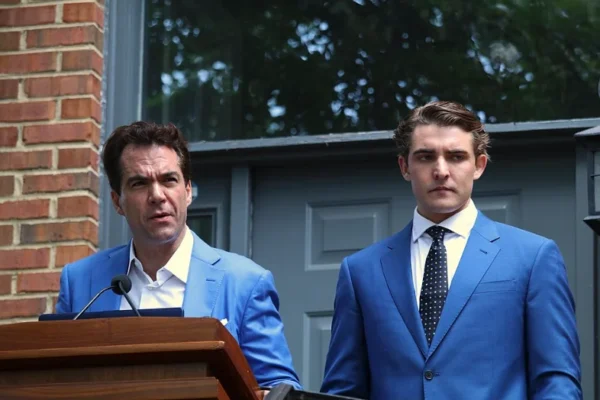
The "Wohl of Wall Street" Returns: Cybersecurity Startup Linked to Infamous Conspiracy Theorists Raises Alarms

A brazen new player in the high-stakes, shadow-filled world of offensive cybersecurity has emerged, promising million-dollar payouts for zero-day vulnerabilities. Yet, behind the polished veneer of the McLean, Virginia-based firm "IRIS C2" lies a far more dubious reality. The startup is the latest venture by Jacob Wohl and Jack Burkman—a duo infamous for a decade-long…

Read Full News

The Digital Markets Act Dilemma: Balancing European Innovation with Cybersecurity Imperatives

In the modern digital economy, the tension between fostering competitive markets and maintaining ironclad data security has reached a critical inflection point. The European Union’s Digital Markets Act (DMA)—a sweeping legislative framework designed to curtail the monopolistic reach of "gatekeeper" platforms—has sparked a fierce debate. While the regulation promises to democratize the digital landscape, tech…

Read Full News

The Fall of a Digital Syndicate: Scattered Spider Key Members Plead Guilty in London

In a landmark development for international cybersecurity enforcement, two young British men—Thalha Jubair, 20, and Owen Flowers, 18—have pleaded guilty to criminal charges related to a devastating August 2024 cyberattack that paralyzed Transport for London (TfL), the backbone of the United Kingdom’s capital transit network. The duo, identified as central figures in the prolific and…

Read Full News