In a stunning development that blurs the lines between cybersecurity defense and digital criminality, federal agents have apprehended a prominent Canadian cybersecurity consultant in Pennsylvania. The arrest, which occurred on October 8, 2026, is a pivotal escalation in the ongoing investigation into the notorious hacking collective known as ShinyHunters. Sources confirm that the individual taken into custody is Edward Dubrovsky, a well-known figure in the industry and co-founder of the cybersecurity firm Cypfer, who was reportedly in Philadelphia to attend a high-profile cyber risk conference.
The arrest of Dubrovsky, who has built a professional reputation on navigating the treacherous waters of ransomware negotiations, represents a potential "insider" breakthrough for the Federal Bureau of Investigation. The Bureau has been under immense pressure following a series of humiliating security breaches—most notably, the theft of sensitive personnel data from an FBI recruitment portal—that ShinyHunters has claimed as their own.
The Arrest: A Conference-Floor Sting
According to reports, the FBI executed the arrest of Dubrovsky during his attendance at the Cyber Risk Summit, held at the Loews Philadelphia Hotel between October 5 and October 7. While the FBI and the Department of Justice have remained tight-lipped regarding the specifics of the operation, court records indicate that Dubrovsky was charged with conspiracy to threaten to impair the confidentiality of information with the intent to extort money, and interference with commerce by threats.
The timing of the arrest is particularly striking. Sources close to the investigation suggest that the FBI’s focus on the ShinyHunters syndicate has been centralized in the Eastern District of Texas, where the investigation is currently being managed. Shortly after his detention, legal filings indicated that the case against Dubrovsky was moved to that district, underscoring the gravity with which federal authorities are treating the link between professional negotiation services and the extortionists themselves.
Chronology of a Global Manhunt
The apprehension of Dubrovsky is the latest in a rapid sequence of events that have dismantled key infrastructure of the ShinyHunters organization over the past several weeks:
- September 2026: Dutch law enforcement officials arrested Pepijn van der Stap, a convicted cybercriminal, in connection with the ShinyHunters probe. The subsequent seizure of his electronic devices provided the FBI with a treasure trove of evidence that effectively turned the tide of the investigation.
- Early October 2026: Following the arrest of Van der Stap, a key figure in the group operating under the pseudonym "Rey"—later identified as a teenager named Saif Al-din Khader—assumed control of the group. "Rey" began a brazen campaign of taunting the FBI, leaking data stolen from the Bureau’s own internal systems.
- October 7, 2026: Reports surfaced detailing the apprehension of Khader, who is currently cooperating with federal investigators. His capture followed a botched extortion attempt targeting a navigation and digital aviation unit divested by Boeing.
- October 8, 2026: Federal agents apprehended Edward Dubrovsky in Philadelphia, marking the transition of the investigation toward those suspected of facilitating the group’s "negotiation" tactics.
The "Negotiator" Dilemma: A Professional Under Scrutiny
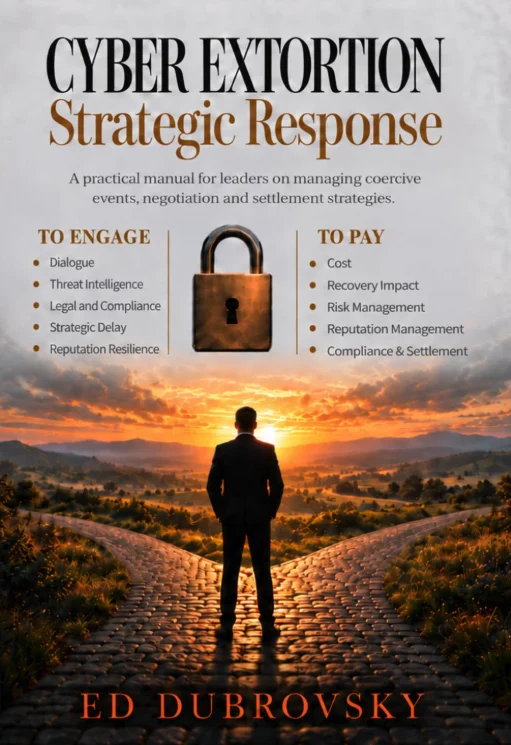
Edward Dubrovsky is no stranger to the world of high-stakes digital extortion. As a co-founder of Cypfer and later an associate with the firm CyberSteward, he positioned himself as an authority on how corporations should handle the volatile landscape of ransomware. His book, Cyber Extortion Strategic Response, is widely cited by industry professionals as a definitive guide to managing the aftermath of a breach.

In the book, Dubrovsky argues that engagement with criminals is a nuanced art. "At the heart of the book is a critical distinction," he wrote. "Communicating with a criminal is not the same as negotiating a payment, and negotiating is not a commitment to pay."
However, the charges filed against him suggest that the FBI believes he crossed that thin, professional line. By charging him with conspiracy to extort, the government is implying that his "advisory" services may have functioned as a mechanism to facilitate or amplify the extortionate demands of the ShinyHunters group rather than merely mitigating them.
Supporting Data: The Rise of ShinyHunters
ShinyHunters has established itself as one of the most prolific and dangerous cyber-syndicates in the modern era. Operating primarily by utilizing sophisticated phishing campaigns and stolen credentials, the group systematically siphons data from software-as-a-service (SaaS) providers. Their modus operandi is ruthless: they threaten to publish sensitive corporate data on public forums unless exorbitant ransom demands are met.
According to FBI estimates, the group has extorted more than $70 million from victims in 2026 alone. The recent theft of FBI recruitment data—which included unit designations, specializations, and even psychiatric records of agents—represented a major intelligence failure that spurred a massive, cross-jurisdictional manhunt.
The complexity of the group’s operations is evidenced by the "Rey" incident, where a teenage operator managed to infiltrate federal systems and publicly mock the Bureau, demonstrating a level of technical sophistication and boldness that forced the FBI to reallocate significant resources to the Texas-based task force.
Official Responses and Legal Status
As of this writing, the FBI has declined to provide a formal statement regarding the specifics of the case against Dubrovsky, citing the ongoing nature of the investigation. FBI Director Kash Patel acknowledged the arrest via a brief social media update, but provided no details on the identity of the suspect or the connection to the broader syndicate.

Dubrovsky is currently being held at a federal facility in Philadelphia. Public records show that he has yet to be assigned a public defender, and he has not yet entered a plea to the charges of conspiracy and extortion. His LinkedIn presence, which until recently featured a post outlining his plans to discuss "compliant driven coercive advisory" at the Philadelphia summit, has become a focal point for investigators looking into his professional network.
Broader Implications for the Cybersecurity Industry
The arrest of a high-profile consultant sends a shockwave through the cybersecurity insurance and negotiation industry. For years, "ransomware negotiators" have operated in a grey area of the law, often acting as intermediaries between criminal groups and victimized corporations. While many firms argue that their work is essential to preventing data leaks and ensuring business continuity, the federal government’s move against Dubrovsky suggests a new, more aggressive regulatory and enforcement posture.
1. The Erosion of Privilege
If the government successfully proves that negotiation firms are acting as conduits for extortion, it may jeopardize the attorney-client or professional privilege that these firms rely upon. Future negotiations could be subject to intense scrutiny, potentially forcing companies to handle incidents with less outside, potentially compromised, assistance.
2. A Warning to Facilitators
This case serves as a stern warning to any professional who might be tempted to move from a position of "defensive advisor" to "facilitator." By targeting individuals who provide the infrastructure for negotiation, the FBI is signaling that it intends to dismantle the entire ecosystem that sustains ransomware groups like ShinyHunters.
3. The Future of Cyber-Insurance
The insurance industry, which frequently foots the bill for these ransoms, may now face increased pressure to distance itself from firms that engage in direct negotiations with known criminal syndicates. This could lead to a massive restructuring of how cyber-insurance policies are written, with stricter compliance requirements regarding who can be hired to respond to a breach.
As the case moves to the Eastern District of Texas, the legal community and the tech industry alike will be watching closely. The outcome of United States v. Dubrovsky will likely define the legal boundaries of incident response for years to come, setting a precedent for how the government treats those who sit across the table from the world’s most dangerous digital criminals. With more charges against other industry principals potentially on the horizon, the, "fast-moving" investigation is far from its conclusion.