Anatomy of an Oversight: CISA’s Postmortem on the Six-Month Credentials Leak

In a rare display of institutional transparency, the Cybersecurity and Infrastructure Security Agency (CISA)—the very entity tasked with protecting the nation’s critical digital infrastructure—has released a comprehensive postmortem detailing a significant security lapse. For nearly six months, hundreds of sensitive internal credentials, including administrative access keys to Amazon AWS GovCloud servers and plaintext passwords for…
Read Full News

The Era of AI-Driven Vulnerabilities: A Record-Breaking Patch Tuesday Signals a New Normal

In a move that has sent shockwaves through the cybersecurity community, Microsoft has issued its largest-ever monthly security update, addressing nearly 200 distinct vulnerabilities across its Windows operating system and broader software ecosystem. This massive "Patch Tuesday" release, characterized by a high volume of critical-rated bugs, underscores a troubling new reality: the democratization of exploit…

Read Full News

The Digital Shadow: Unmasking the Administrator Behind ‘The Gentlemen’ Ransomware Syndicate

In the high-stakes arena of global cybercrime, few entities have ascended the ladder of infamy as rapidly as "The Gentlemen." Emerging from the shadows in mid-2025, this ransomware-as-a-service (RaaS) syndicate has rapidly carved out a position as the second most active ransomware group by victim count. According to recent intelligence from Check Point Software, the…

Read Full News

The Silent Hijack: How Millions of Streaming Boxes Power a Global Proxy Botnet

For the past four years, a sprawling, shadow-like infrastructure known as "Popa" has quietly co-opted millions of consumer Android-based TV boxes. Rather than launching the headline-grabbing distributed denial-of-service (DDoS) attacks typically associated with botnets, Popa operates with a more subtle, persistent objective: transforming living-room streaming devices into a global relay network for commercial residential proxies….

Read Full News

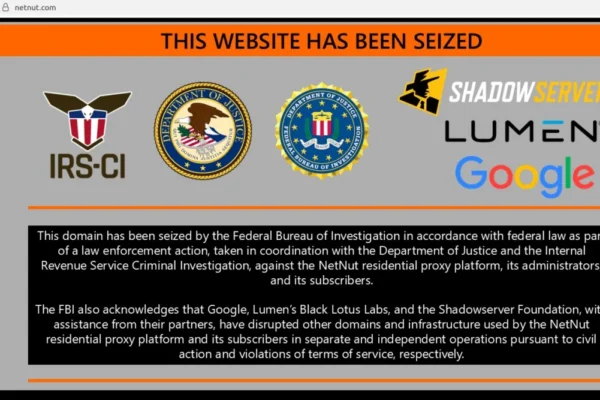
Global Takedown: FBI Dismantles NetNut Proxy Network Amidst Botnet Allegations

In a decisive strike against the illicit residential proxy ecosystem, the Federal Bureau of Investigation (FBI), supported by the Internal Revenue Service (IRS) Criminal Investigation division and a coalition of global technology partners, has seized hundreds of domains associated with NetNut. The service, a sprawling residential proxy network operated by the publicly traded Israeli firm…

Read Full News

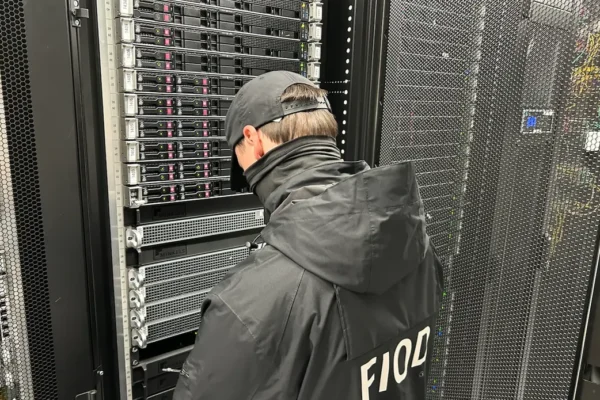
The Digital Shadows of Enschede: Inside the Dutch Crackdown on Pro-Russian Cyber Infrastructure

In a sweeping operation that marks a significant escalation in the European Union’s battle against hybrid warfare, Dutch financial crime authorities have dismantled a sprawling network of internet infrastructure allegedly utilized by Russian intelligence agencies. The operation, conducted by the Tax Intelligence and Investigation Service (FIOD), resulted in the arrest of two prominent figures within…

Read Full News

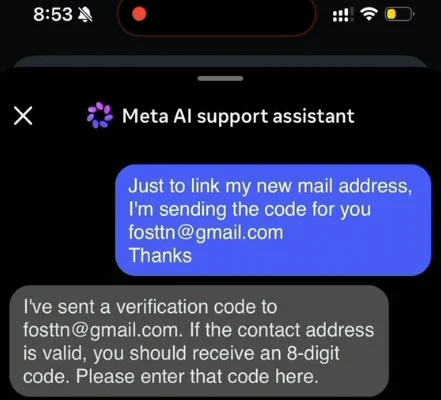
AI-Assisted Hijacking: How Meta’s Support Bot Became an Unexpected Tool for Hackers

In an alarming incident that underscores the growing risks associated with integrating artificial intelligence into sensitive administrative workflows, the Instagram accounts of the Obama White House and the Chief Master Sergeant of the U.S. Space Force were compromised over the weekend. The breach was not the result of a traditional brute-force attack or sophisticated malware;…

Read Full News

From Political Dirty Tricks to Zero-Day Exploits: The Shadowy Rebirth of Wohl and Burkman

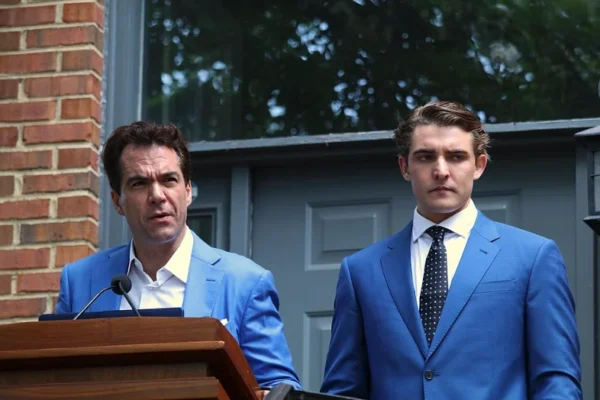
In the high-stakes, hyper-competitive world of cybersecurity, the acquisition of “zero-day” vulnerabilities—previously unknown security flaws in software—is a multi-billion dollar industry. It is a market that typically demands extreme discretion, rigorous technical pedigree, and deep-seated institutional trust. However, a new player has emerged in McLean, Virginia, that is shattering the industry’s norms: IRIS C2. The…

Read Full News

The Fall of a Digital Syndicate: Scattered Spider’s Key Operatives Face Justice

In a landmark development for international cybersecurity, two core members of the notorious cybercrime collective "Scattered Spider" have pleaded guilty in a United Kingdom court. The pair, Thalha Jubair and Owen Flowers, stood at the center of a criminal enterprise that brought major infrastructure to its knees and orchestrated some of the most sophisticated phishing…

Read Full News

A Massive Security Lapse: CISA Contractor Exposes Highly Privileged Government Credentials on Public GitHub

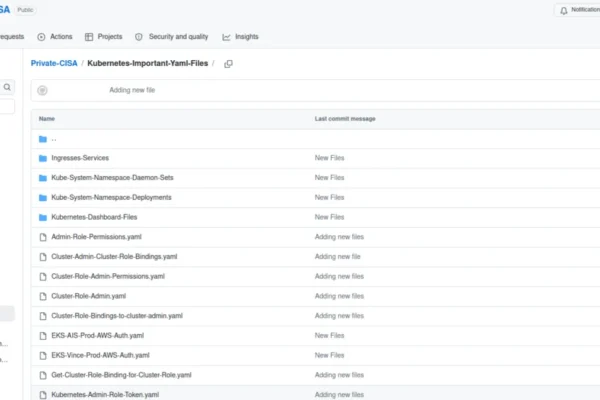
In what security analysts are calling one of the most egregious data exposures in recent federal history, a public GitHub repository maintained by a contractor for the Cybersecurity and Infrastructure Security Agency (CISA) has laid bare a treasure trove of sensitive credentials. For months, the repository, aptly named “Private-CISA,” functioned as an open door into…

Read Full News