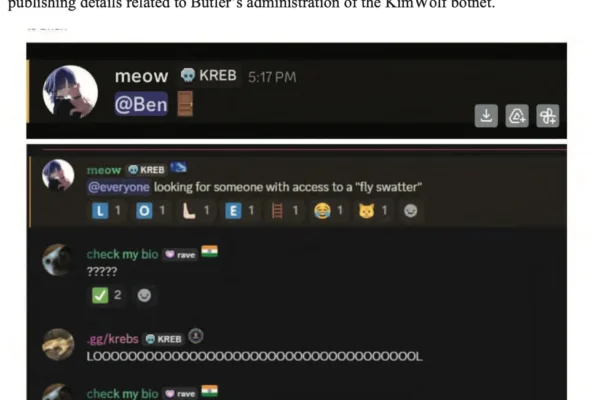
The Fall of ‘Dort’: Inside the Collapse of the Kimwolf IoT Botnet

In a landmark victory for international law enforcement, a 23-year-old Ottawa resident, Jacob Butler—known in the shadowy corners of the internet by the handle "Dort"—was arrested this week on charges of masterminding "Kimwolf," a formidable Internet-of-Things (IoT) botnet responsible for a wave of record-breaking cyberattacks that have plagued global networks for the past six months….
Read Full News

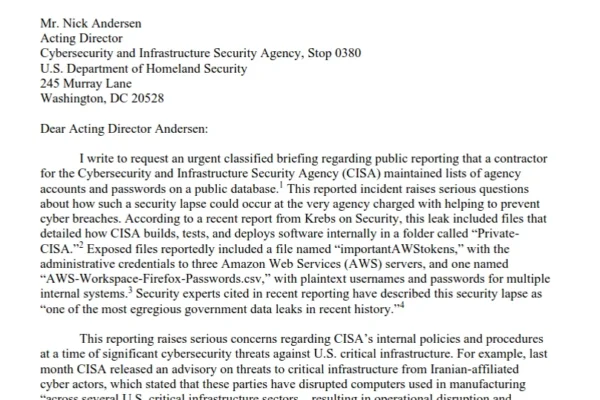
Federal Security Crisis: Congressional Leaders Demand Accountability Following Massive CISA Data Leak

The U.S. Cybersecurity and Infrastructure Security Agency (CISA)—the very entity tasked with safeguarding the nation’s digital defenses—is currently reeling from a major security breach. A contractor with administrative access to the agency’s development infrastructure intentionally published a trove of sensitive credentials, including AWS GovCloud keys and internal system passwords, on a public GitHub repository. The…

Read Full News

The AI Arms Race: Microsoft’s Record-Breaking Patch Tuesday Signals a New Era of Vulnerability

In a landmark event that underscores the accelerating volatility of the global digital landscape, Microsoft released a massive suite of security updates today, addressing nearly 200 vulnerabilities across its Windows ecosystem and associated software. This monthly "Patch Tuesday" cycle marks a historical high-water mark for the software giant, signaling that the sheer volume of discovered…

Read Full News

The Rise of "The Gentlemen": How an Aggressive Ransomware Syndicate Fueled a Global Cybercrime Surge

In the shadows of the dark web, a new force has ascended to the top tier of the global ransomware hierarchy. Known as "The Gentlemen," this Ransomware-as-a-Service (RaaS) syndicate has rapidly transformed from an obscure threat actor into the second most active ransomware operation in the world. By shattering industry conventions and aggressively recruiting talent…

Read Full News

The Silent Hijack: How Millions of Streaming Boxes Power a Global Proxy Botnet

For the past four years, an expansive and largely invisible infrastructure known as the Popa botnet has quietly co-opted millions of consumer Android-based TV boxes. These devices, often purchased for their ability to stream subscription video content for a one-time fee, are being weaponized to relay massive volumes of internet traffic. Security researchers have now…

Read Full News

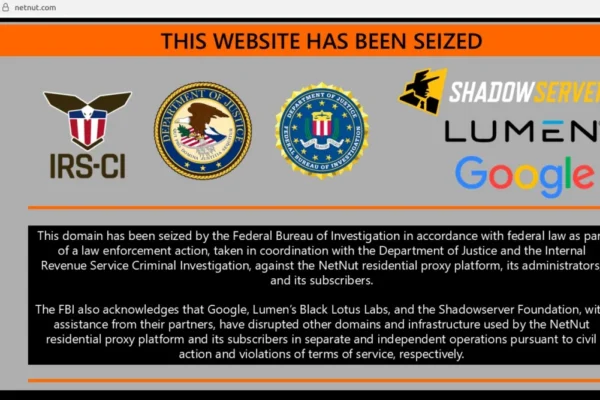
The Fall of NetNut: FBI Dismantles Global Proxy Network Linked to Millions of Compromised Devices

In a significant blow to the cybercrime ecosystem, the Federal Bureau of Investigation (FBI) has successfully seized hundreds of domains associated with NetNut, a sprawling residential proxy service operated by the publicly traded Israeli company Alarum Technologies [NASDAQ: ALAR]. The takedown, executed in coordination with the Internal Revenue Service Criminal Investigation (IRS-CI) and a coalition…

Read Full News

The AI Security Paradox: How Anthropic’s "Project Glasswing" is Rewriting the Patching Playbook

The landscape of cybersecurity is undergoing a seismic shift, driven by a paradoxical reality: while artificial intelligence platforms are increasingly being targeted by sophisticated social engineering, they have simultaneously become the most potent tools in the defender’s arsenal. This month, the global tech industry is witnessing the tangible consequences of this shift as software titans—including…

Read Full News

Digital Proxies of War: The Dutch Crackdown on Infrastructure Powering Russian Cyber-Operations

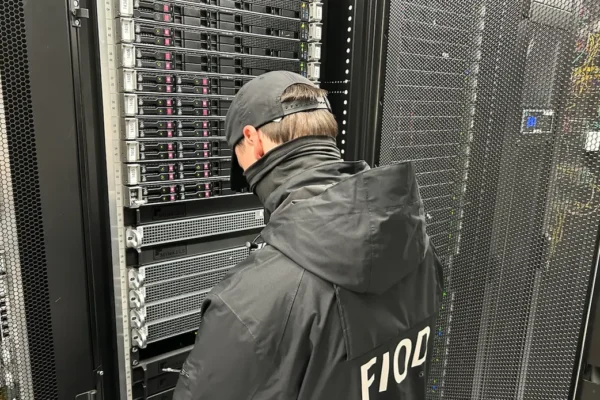
In a significant blow to the clandestine digital infrastructure supporting the Kremlin’s hybrid warfare, Dutch financial crime investigators have executed a high-profile raid, dismantling a network accused of facilitating Russian cyberattacks and disinformation campaigns across the European Union. On May 18, the Fiscal Intelligence and Investigation Service (FIOD) arrested two primary figures linked to the…

Read Full News

The Downfall of Scattered Spider: Two British Hackers Plead Guilty to Global Cyber-Terrorism

In a landmark development for international cybercrime enforcement, two key members of the notorious hacking collective "Scattered Spider" have pleaded guilty in a United Kingdom court. The pair, Thalha Jubair, 20, and Owen Flowers, 18, admitted to a string of devastating cyberattacks that crippled critical infrastructure, including London’s public transport network, and compromised major healthcare…

Read Full News